The virtual cybersecurity department for startups.

Replace your compliance tool, fractional CISO, and patchwork in between.

Humans, powered by AI.
Sargam Bansal, Co-Founder & CEO
Scroll

Your security posture. Live, every morning.

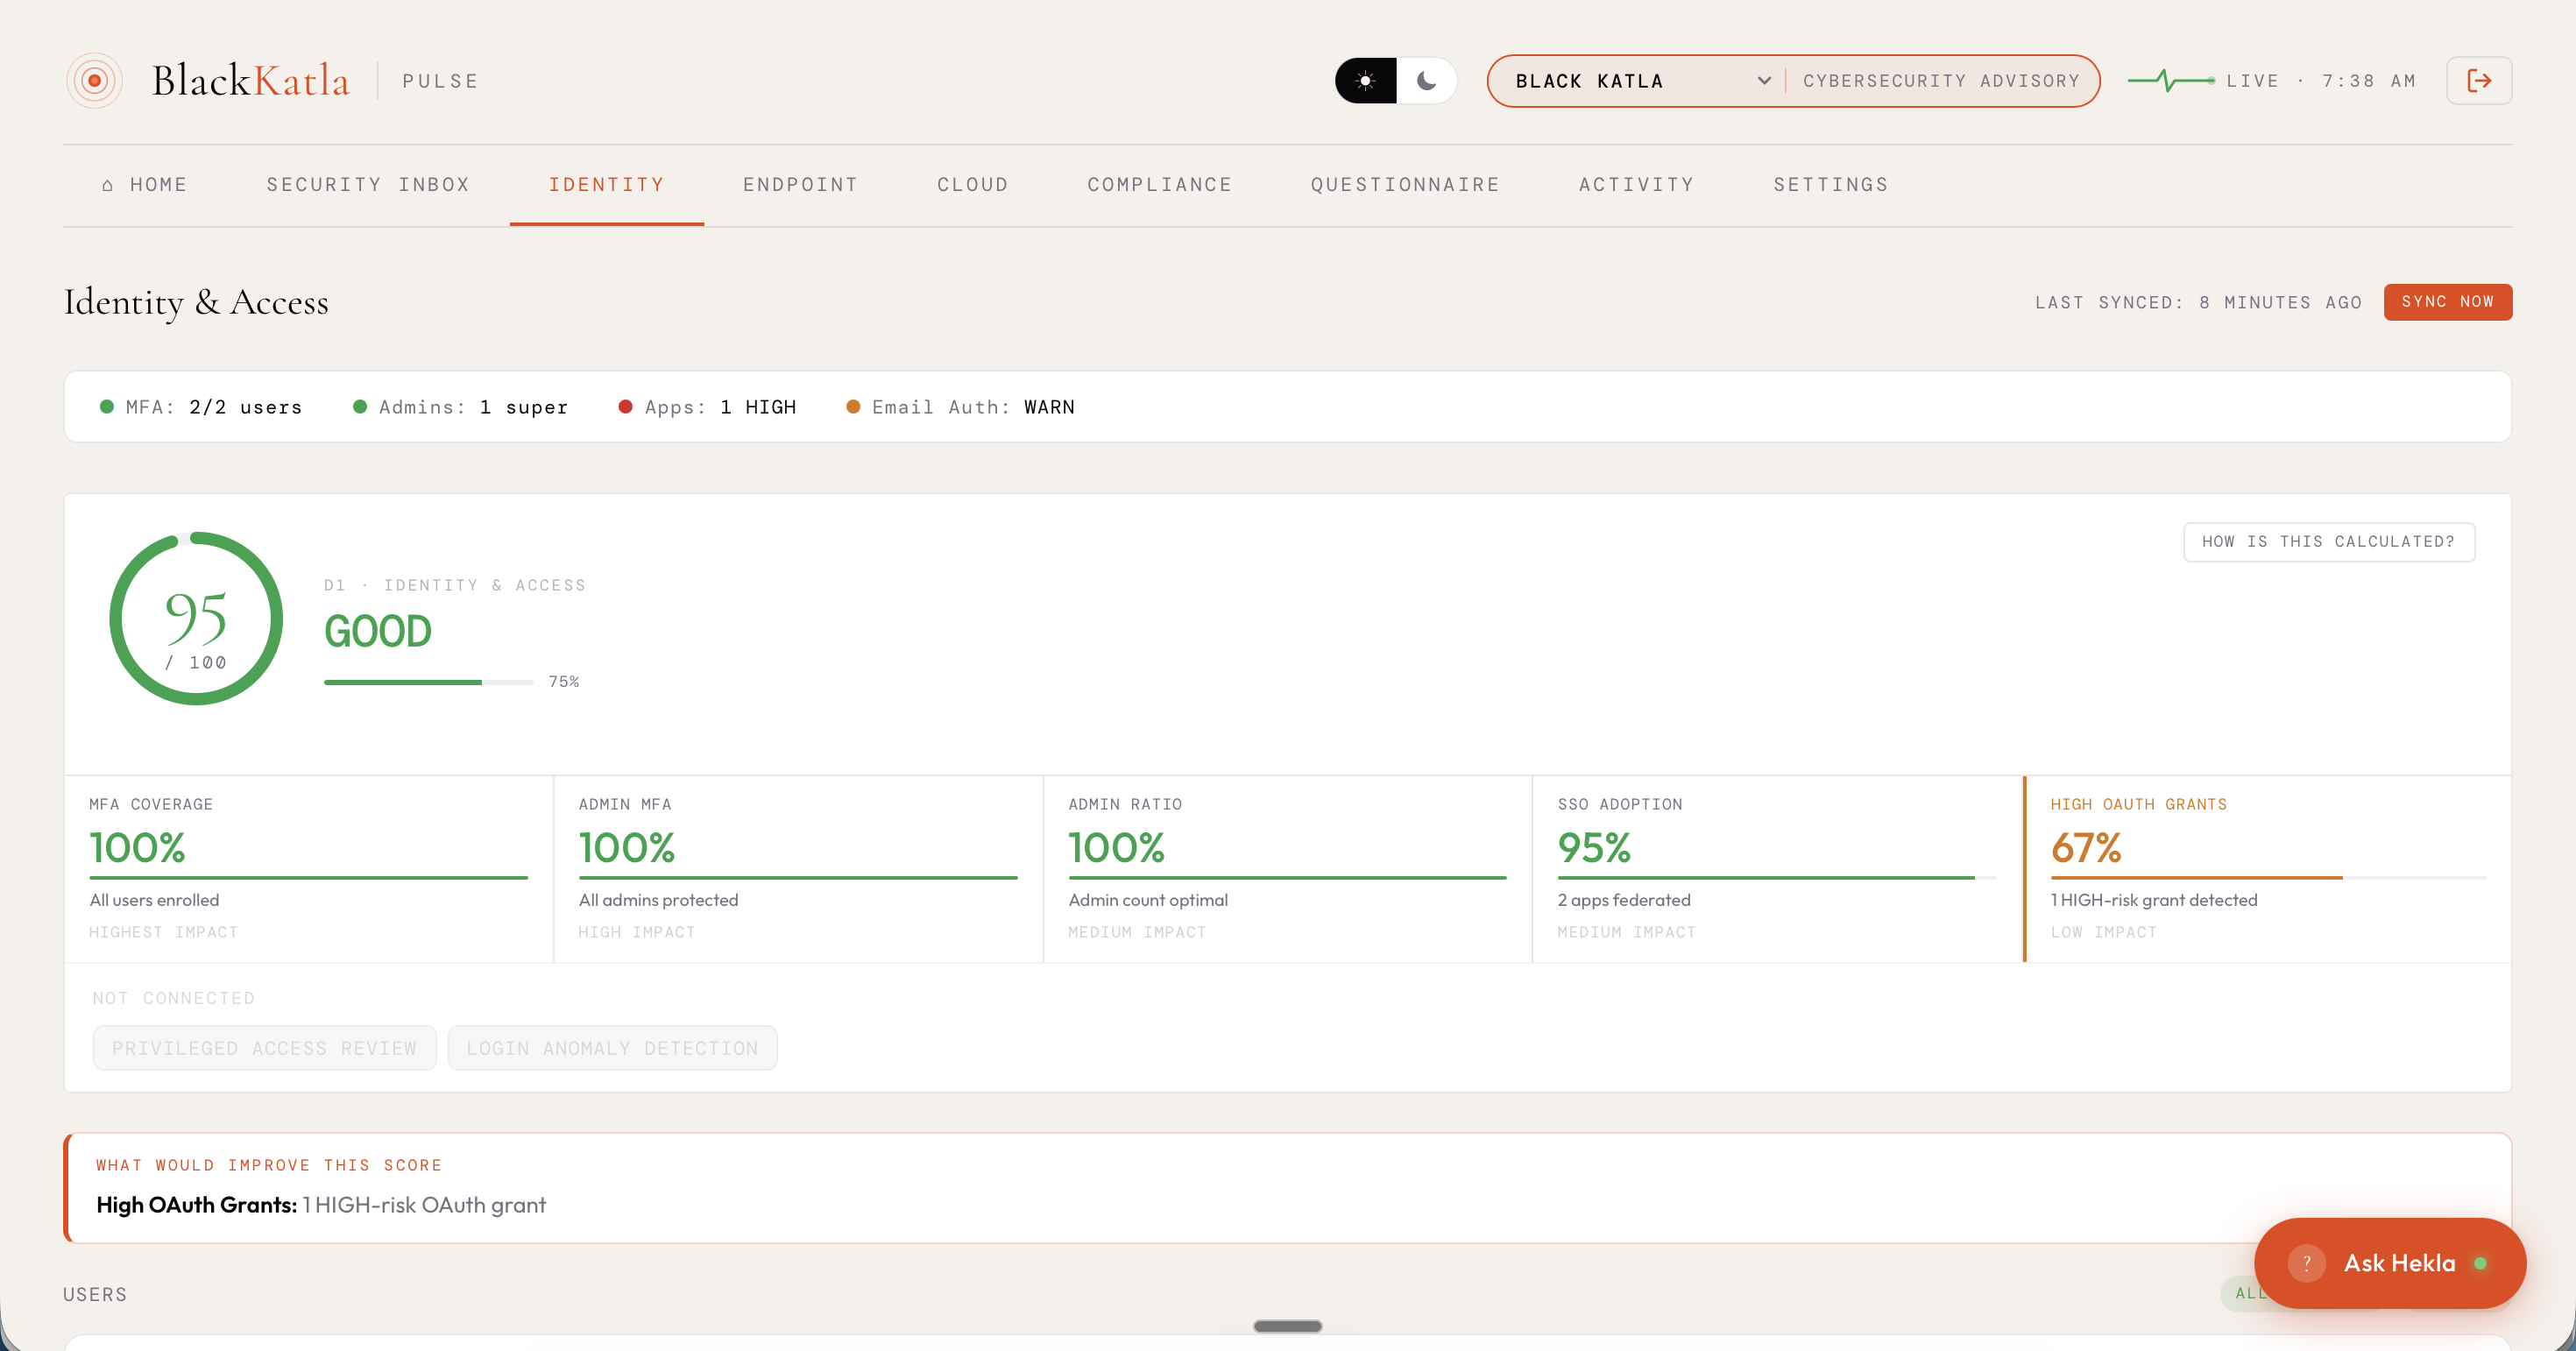
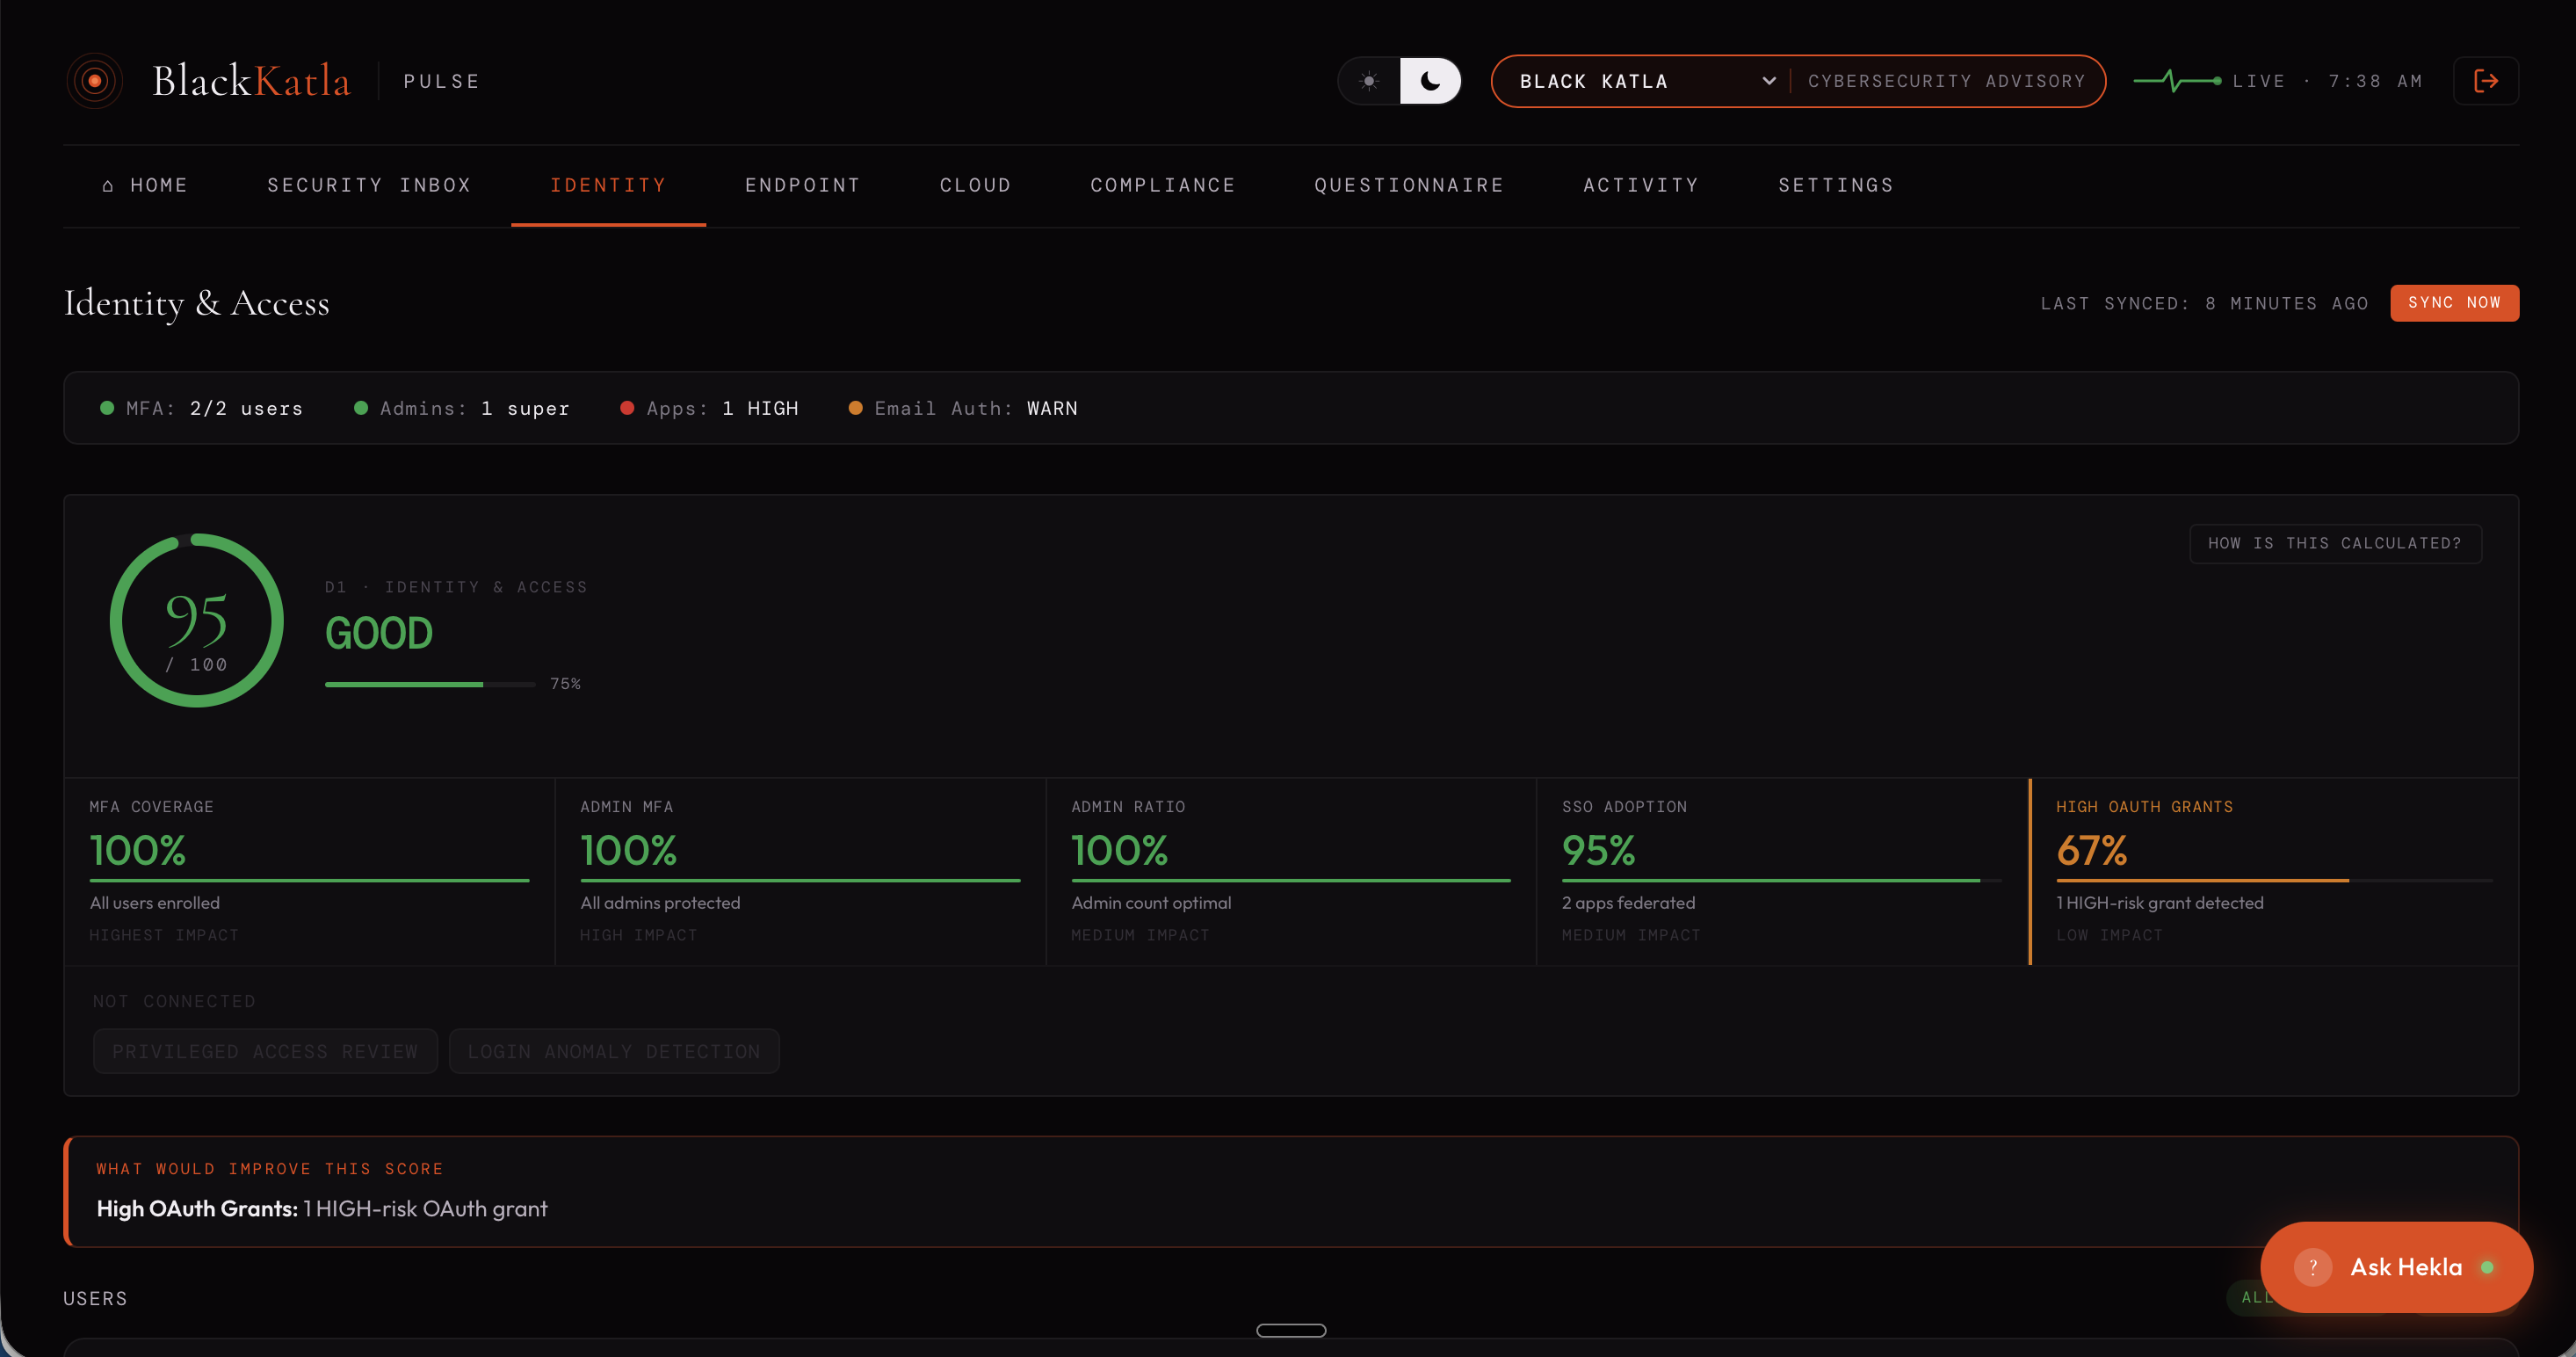
Most founders learn about a gap when a prospect asks a question they can't answer. Katla Pulse flips that — it monitors your real environment every day, scores it across seven security domains, and tells you the three things worth fixing this week. Not a questionnaire. Not a certificate. The actual state of your security, this morning.

Three scores, daily

Security Health, Audit Readiness, Breach Resilience. Read from your real environment every 24 hours.

Named findings

Every gap is a specific user, device, or resource. What the risk is, what the worst case looks like, the one move that closes it.

Questionnaires answered

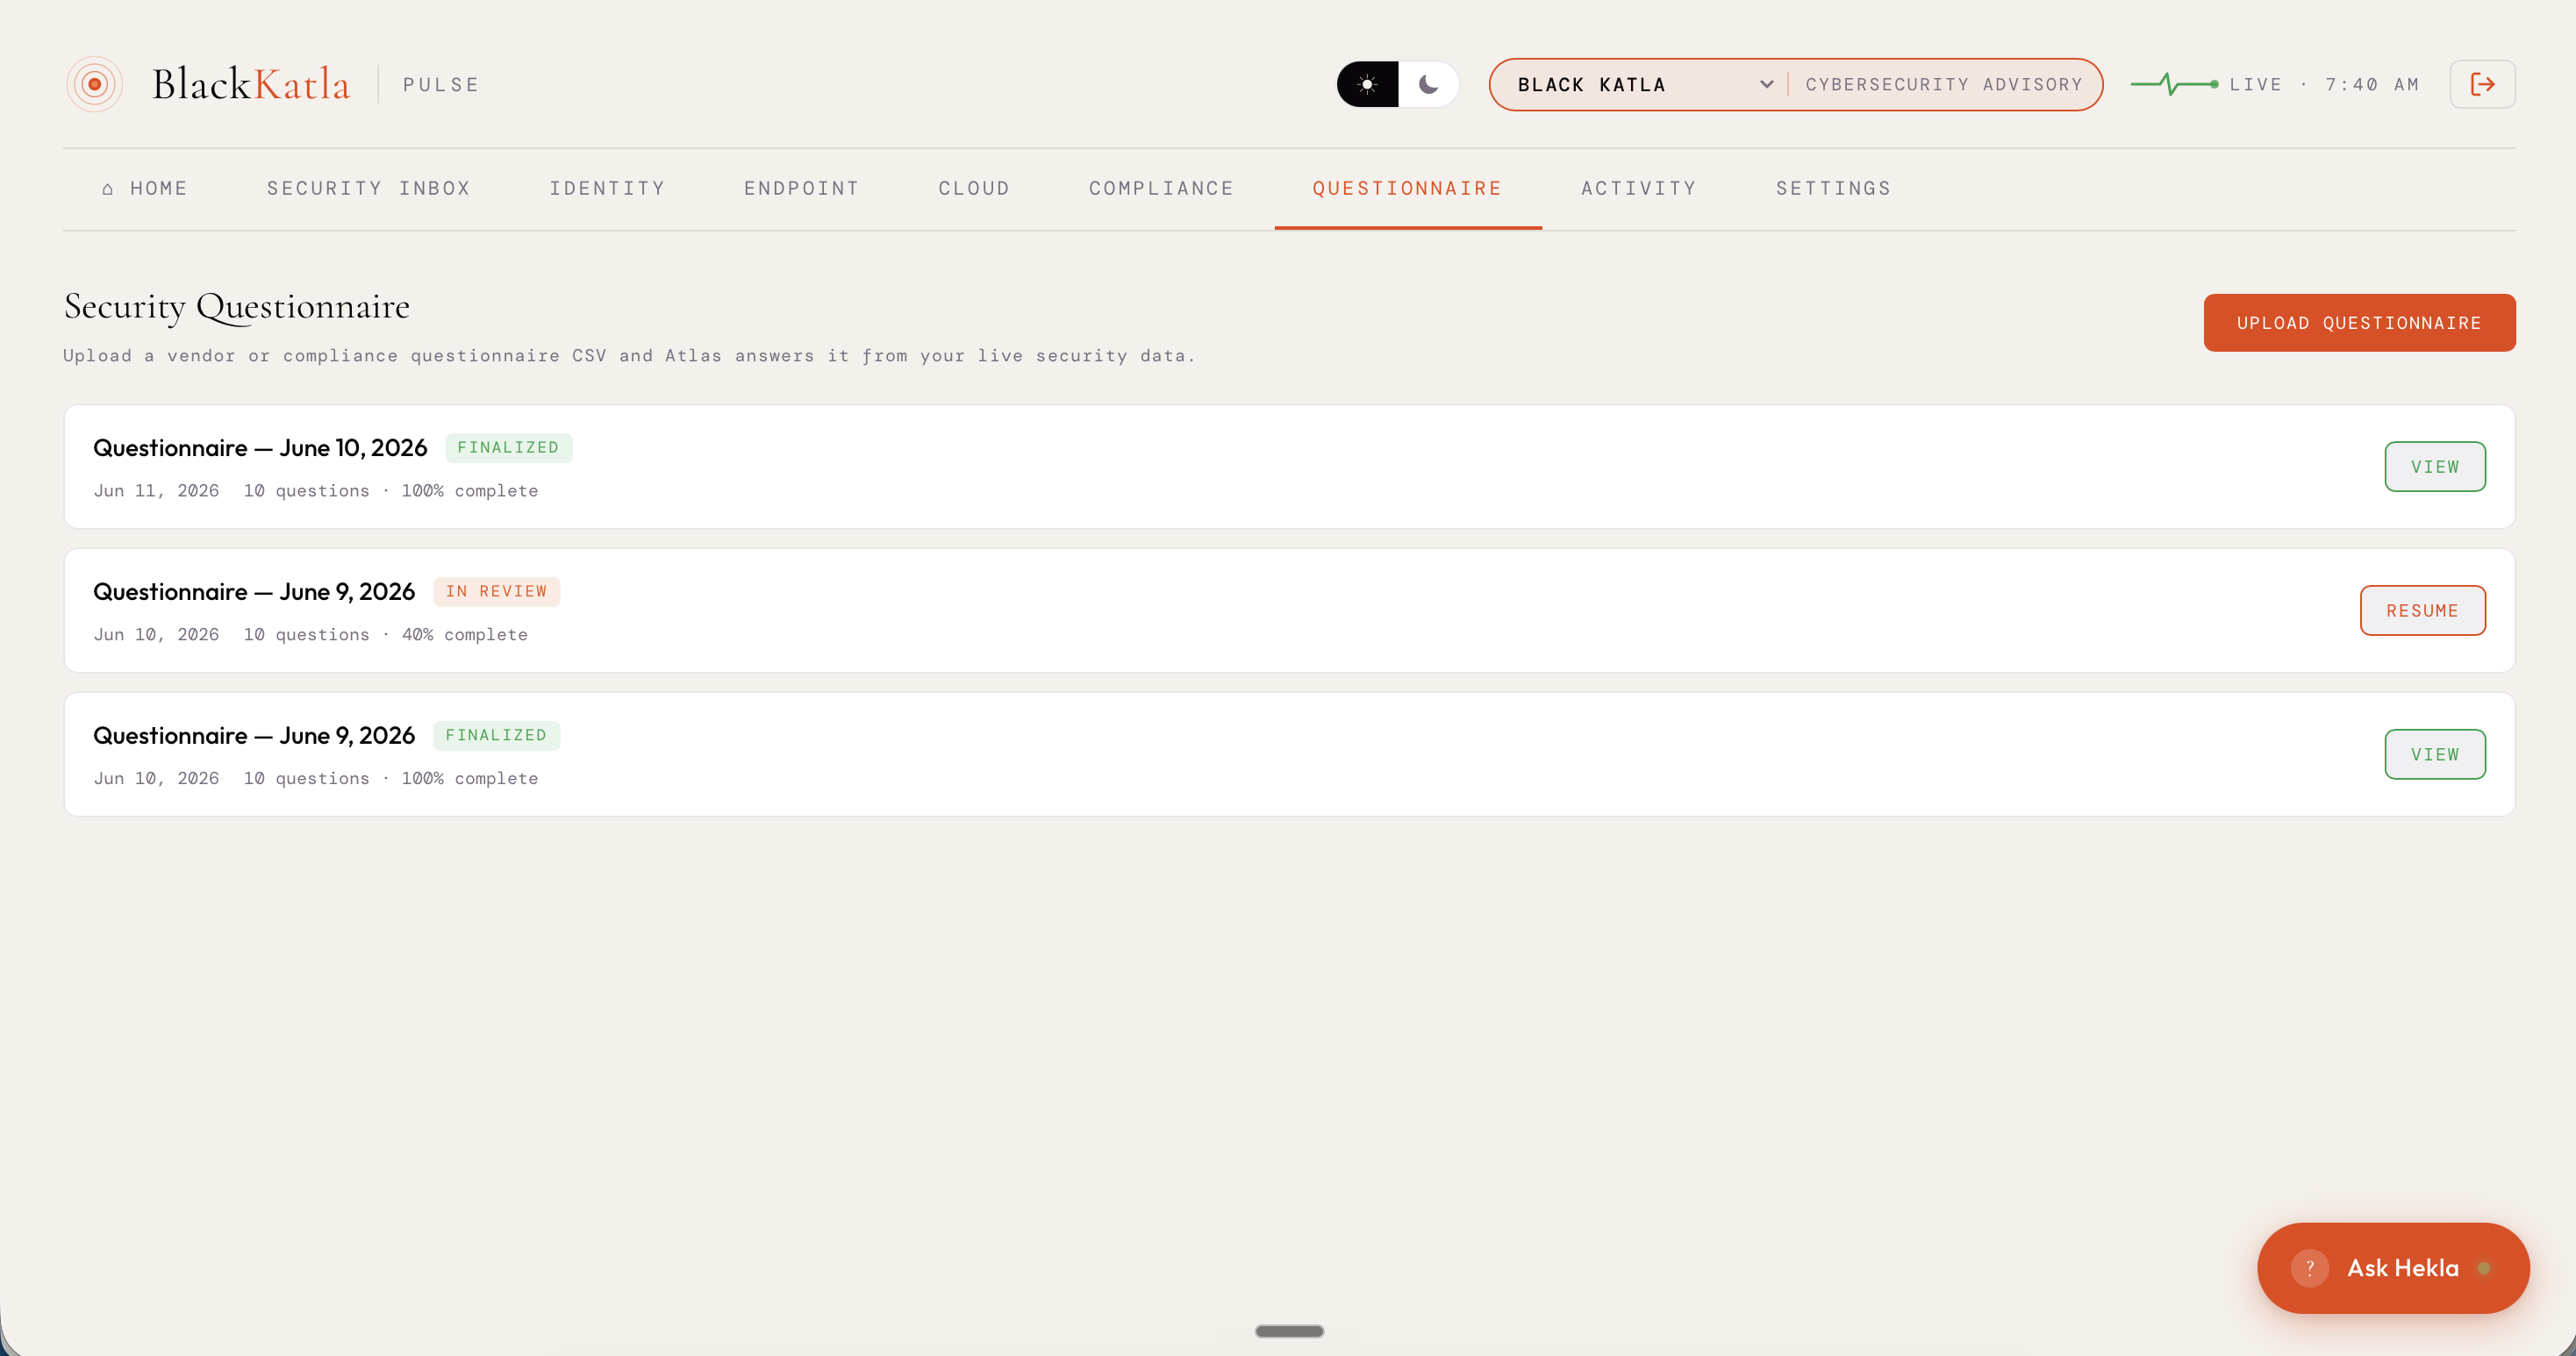
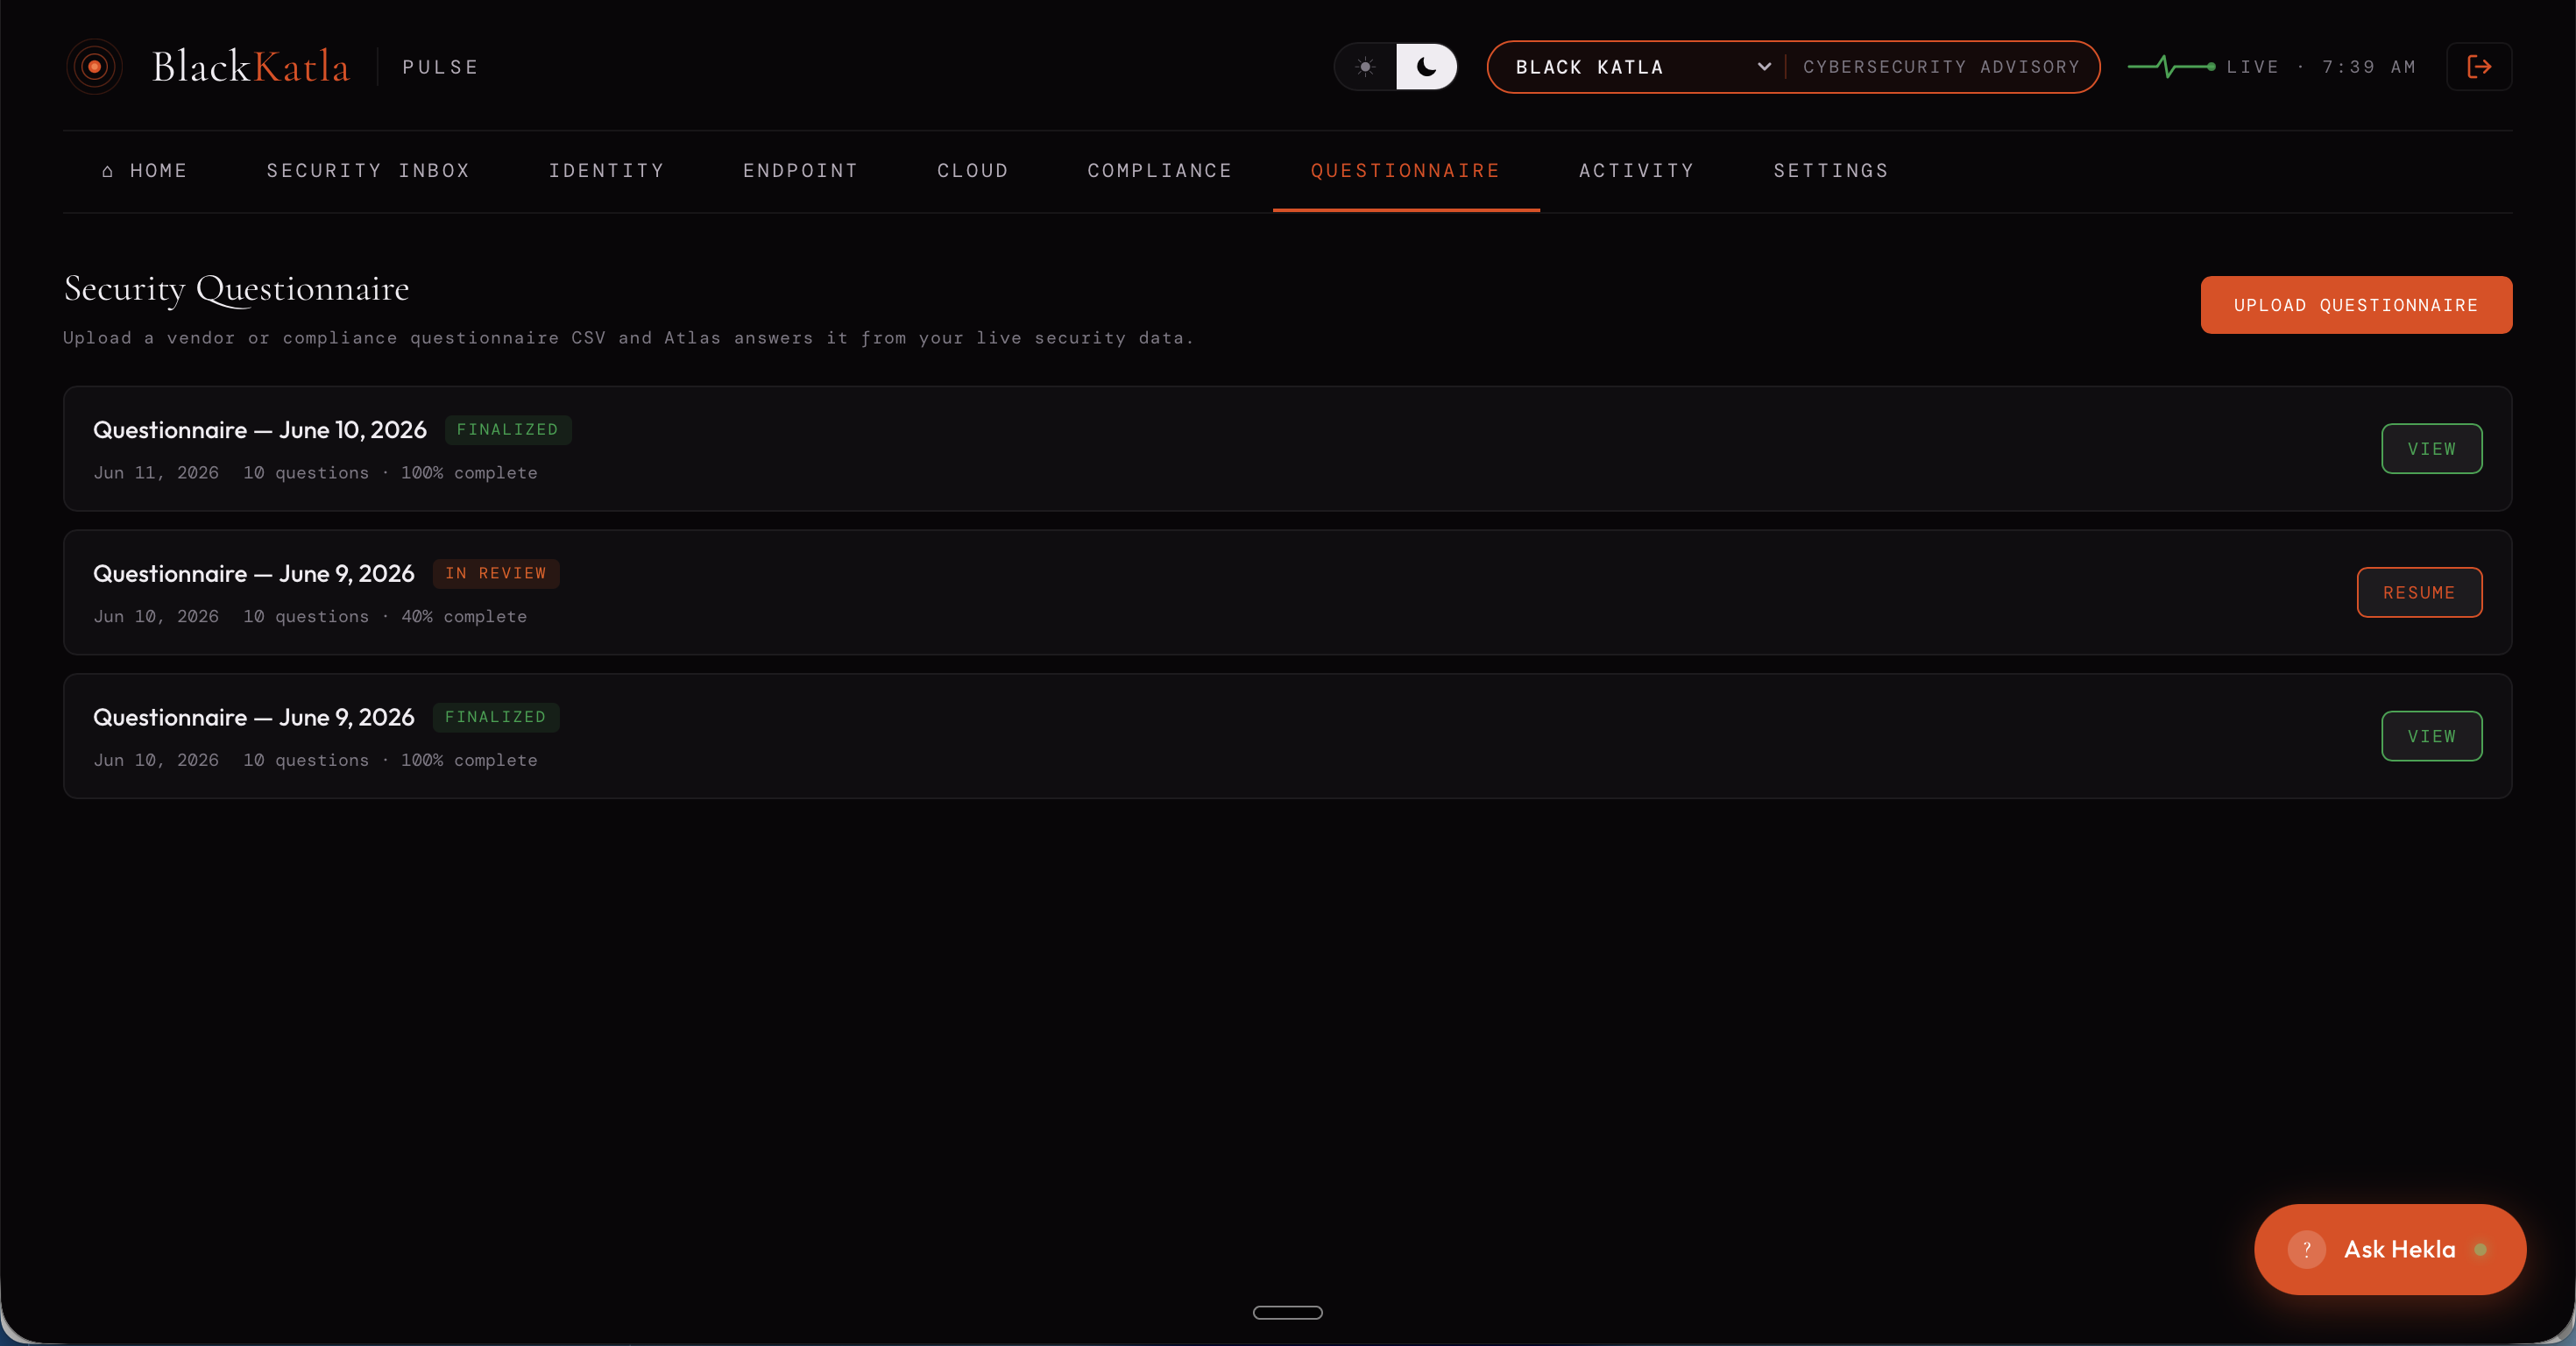
Upload the security review blocking your deal. Answered from live signal, not guesswork. 48-hour turnaround.

A cybersecurity department isn't one thing. It's seven.

Most security vendors sell one of these. Founders are left to assemble the rest.

90
Days to Audit-Ready
24/7
Monitoring Coverage
4hr
Security Incident Response
48hr
Customer Questionnaire Response
01
Strategy & Governance

Security strategy, policies, risk management, board and investor reporting.

02
Engineering Security

Application security, infrastructure security, secure architecture, working alongside developers.

03
Operations

24/7 monitoring, endpoint protection, incident response, threat detection.

04
Compliance

SOC 2, HIPAA, PCI-DSS. Audit management. Evidence collection. Auditor liaison.

05
Business Interface

Customer security questionnaires. RFP and contract review. Customer security calls. Sales enablement.

06
Resilience

Business continuity, disaster recovery, tabletop exercises, incident response playbooks.

07
External Intelligence

Cyber threat intelligence, regulatory monitoring, vendor and third-party risk.

Building all seven in-house takes years and millions.

The full security department. One flat retainer.

SOC 2 is a driver's license. It proves you passed a test once. It doesn't make you a safe driver. BlackKatla is the safe-driving program — and SOC 2 is just one of the licenses we help you get along the way.

01
Katla Pulse dashboard — live security scores across 7 domains, daily Morning Brief, Security Inbox with named findings, questionnaire engine
02
vCISO leadership — strategic direction, board and investor reporting, security roadmap ownership. A named security leader for your company.
03
SOC 2 program ownership — we own the audit end to end. Gap assessment, evidence collection, auditor management, zero findings goal.
04
HIPAA / PCI-DSS programs — if your environment requires it, we run it. We tell you which audits you actually need — and push back on the ones you don't.
05
24/7 SOC monitoring — human-reviewed threat detection across endpoints, identities, and cloud. Huntress-powered EDR. Not just alerts — response.
06
Incident response — 4-hour SLA. We take the call, run the playbook, handle the communication. You focus on the product.
07
Security questionnaire response — 48-hour SLA on customer security reviews. Answered from live Katla Pulse signal. Your engineers stay in their lane.
08
Endpoint protection — EDR deployed and managed across your fleet. Every device covered, every agent current.
09
Cloud security posture — continuous monitoring across AWS, GCP, Azure, and Cloudflare. Misconfigurations caught before they become incidents.
10
Customer security calls — we join the call with your enterprise prospect. You don't have to be the one answering hard security questions.
11
Vendor and access reviews — quarterly. Who has access to what, and whether they should.
12
Monthly posture report — board and investor ready. The security update your Series B investors will ask for.

A CISO earns $300,000–$500,000 per year before equity. That's the salary alone — before tools, before team, before the two years it takes to build a real program. BlackKatla is the full department, running from week one, at $144,000 per year.

From $12,000/month · Scope-dependent · Schedule a call for details.

Most engagements begin within two weeks of kickoff.

What you'd otherwise be doing.

Most startups face two real alternatives. Here's how each compares.

Hiring In-House
BlackKatla
DIY Stack
What It Is
One senior security hire, plus tools and team you build out
A complete cybersecurity department on retainer
Compliance tool + fractional CISO + managed SOC + EDR + CSPM, stitched together
Annual Cost
$500K–$750K+ for a real function
$144,000 (from $12,000/month)
$170K–$400K depending on choices
Time to Audit-Ready
6–12 months from hire date
90 days from kickoff
6–12 months coordinating vendors
Vendors to Manage
One team to recruit, manage, and retain
One team. Us.
4–5 vendors, your CTO coordinates
Developer Time
Some pull-in for audit walkthroughs and technical evidence — your hire takes the rest
Some pull-in for technical walkthroughs — we handle questionnaires, auditor management, customer security calls
Still significantly pulled. The tools don't answer questionnaires; the fractional CISO doesn't have the bandwidth.
Accountability
Sits with your hire — until they leave
One team owns the outcome
Diffused. Each vendor blames the next.
Coverage
All seven functions, business hours. 24/7 means hiring 4+ more people.
All seven functions. 24/7 monitoring included.
Whatever your stack covers. 24/7 means adding another vendor on top.
Hidden Costs
Recruiting, equity, churn, ramp time
None. The price is the price.
Your CTO's time managing five vendors
BlackKatla
What It IsA complete cybersecurity department on retainer
Annual Cost$144,000 (from $12,000/month)
Time to Audit-Ready90 days from kickoff
Vendors to ManageOne team. Us.
Developer TimeSome pull-in for technical walkthroughs — we handle questionnaires, auditor management, customer security calls
AccountabilityOne team owns the outcome
CoverageAll seven functions. 24/7 monitoring included.
Hidden CostsNone. The price is the price.
Hiring In-House
What It IsOne senior security hire, plus tools and team you build out
Annual Cost$500K–$750K+ for a real function
Time to Audit-Ready6–12 months from hire date
Vendors to ManageOne team to recruit, manage, and retain
Developer TimeSome pull-in for audit walkthroughs and technical evidence — your hire takes the rest
AccountabilitySits with your hire — until they leave
CoverageAll seven functions, business hours. 24/7 means hiring 4+ more people.
Hidden CostsRecruiting, equity, churn, ramp time
DIY Stack
What It IsCompliance tool + fractional CISO + managed SOC + EDR + CSPM, stitched together
Annual Cost$170K–$400K depending on choices
Time to Audit-Ready6–12 months coordinating vendors
Vendors to Manage4–5 vendors, your CTO coordinates
Developer TimeStill significantly pulled. The tools don't answer questionnaires; the fractional CISO doesn't have the bandwidth.
AccountabilityDiffused. Each vendor blames the next.
CoverageWhatever your stack covers. 24/7 means adding another vendor on top.
Hidden CostsYour CTO's time managing five vendors

From kickoff to confident. In 90 days.

Most security programs take years to build because nobody owns the outcome. We do. From day one, Katla Pulse is live in your environment — reading your posture, surfacing findings, answering questionnaires. The 90 days are how we build the program around it.

PHASE 1 · WEEKS 1–2
Your environment, mapped.

Katla Pulse connects to your identity, endpoint, and cloud infrastructure. Early in week one you have a live security score. We name every gap, rank it by impact, and tell you which ones will kill a deal or an audit.

PHASE 2 · WEEKS 3–6
Your program, built.

Policies written to match your actual controls. Governance backbone in place. SOC 2 (or HIPAA, or PCI-DSS — whichever applies) scoped and the audit timeline set. Your vCISO is your named security leader from this point forward.

PHASE 3 · WEEKS 7–10
Your environment, hardened.

Huntress EDR deployed across your fleet. Cloud baselines set. Identities secured. Evidence collection running automatically. Katla Pulse scores moving.

PHASE 4 · WEEKS 11–12
Audit-ready. Confirmed.

Tabletop exercise. Full audit-readiness review. Every control tested. Every evidence request answered. By week 12 you're ready for a SOC 2 audit, an enterprise security review, or a Series B due diligence — whichever comes first.

24/7 monitoring runs from week one. The department doesn't stop when the audit does.

"Katla has been erupting for over 6,700 years. The next eruption is coming. They just don't know when."

BlackKatla is named for Iceland's most feared subglacial volcano — dormant beneath ice, overdue, catastrophically powerful when it moves. In security, the breach that destroys companies is never the one you expected. It's the one building silently for years. We are the team that sees what's building before it surfaces.

Sargam Bansal
Co-Founder & CEO
20 years building and running security programs across banking, payments, healthcare, and energy. Has stood up security and compliance programs from scratch three times, across very different industries — most recently for a retail subsidiary post-divestiture. Then led PCI compliance and cloud security across a $1B corporate payments portfolio at WEX — zero audit findings, 100% control-defense rate in external audits.
BK

Tell us what's pressing.

Whether you're staring down a SOC 2 deadline, prepping for a Series B, or just got a 200-question security questionnaire from a prospect — tell us what's pressing. We'll give you a direct answer.

✉ hello@blackkatla.com
⏱ Direct — under 4 hours

No spam. No sales team. Direct response within 4 hours.

Message received.

We'll respond personally within 4 hours.